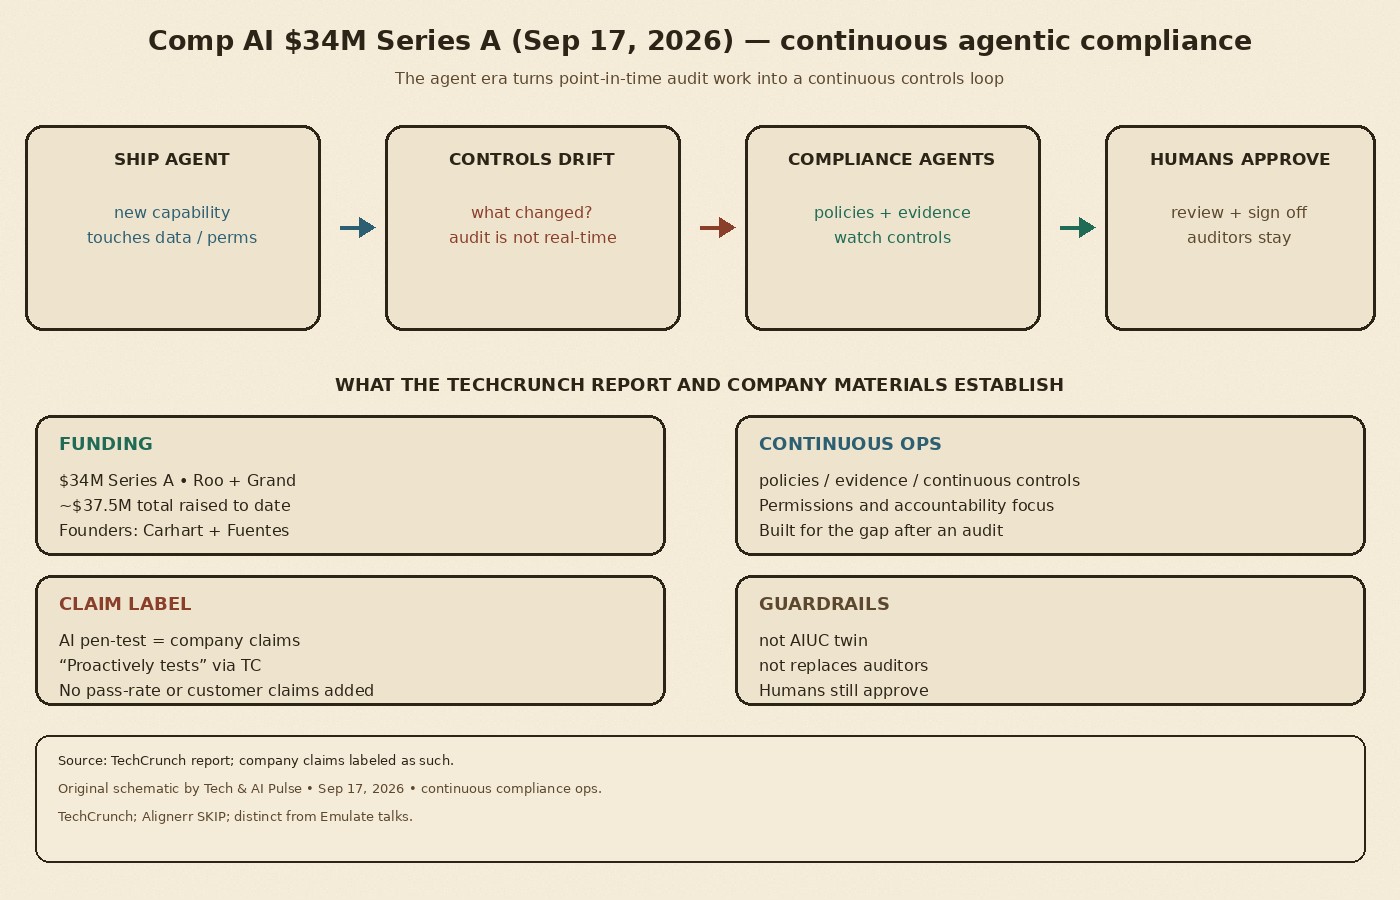
From Mexico — don’t read this as another “SOC 2 checkbox” press release. TechCrunch reports Comp AI raised a $34 million Series A led by Roo Capital and Grand Ventures (~$37.5M total to date) for continuous compliance ops tooling: agents that help draft policies, collect audit evidence, and watch whether controls still hold after you ship new agents. That’s ops tooling — not an AIUC-style certification standard, and not “replaces auditors.”
The founders’ own LeapAI chapter is the color: they felt how tedious SOC 2 work gets when you’re trying to close bigger deals. Comp AI is the bet that compliance work should stay continuous when product (and AI agents) keep changing.
Continuous ops — policies, evidence, controls
Per TechCrunch, Comp AI’s agentic platform helps with the tedious security and compliance stack: write company security policies, collect evidence for security audits, and continuously monitor whether the company is meeting compliance controls. CEO Lewis Carhart’s frame: for a lot of software companies, security and compliance are directly tied to revenue — a customer asking for a SOC 2 report before closing a deal.
I’m sticking to what TC lists. No invented customer logos or pass rates.
Humans still approve — not “replaces auditors”
Carhart told TechCrunch the software helps meet and maintain requirements but doesn’t replace independent audit review. Humans still onboard the AI, support controls, and keep the workflow honest. An agent might draft a policy; a person still reviews and approves it. As agents take on more consequential actions, the trio says safeguards and human approval should increase — I’m quoting the product stance, not inventing one.
AI pen-testing — company claim, labeled
Comp AI also offers AI-powered penetration testing that, in Carhart’s words to TechCrunch, “proactively tests codebases and infrastructures for vulnerabilities.” That’s a company claim via TC — I’m labeling it, not endorsing a bake-off score.
Why continuous — the agent-era gap
Carhart’s example in the piece: finish a SOC 2 audit, then two weeks later ship a new AI agent that can touch customer data, change permissions, or introduce a vulnerability. The audit didn’t become invalid — it just wasn’t designed to tell you in real time what changed afterward. Mariano Fuentes adds the accountability angle: show what an agent accessed, what it tried, and whether it stayed in bounds. Comp AI says it’s starting with permissions and accountability toward continuous monitoring. Soft Vanta/Drata category color only — I’m leading the continuous-ops / agent-drift frame, not a feature matrix.
$34M Series A — Roo + Grand
TechCrunch: $34 million Series A led by Roo Capital and Grand Ventures; ~$37.5 million raised to date. Founded last January by Lewis Carhart (CEO), Claudio Fuentes (COO), and Mariano Fuentes (CTO). Proceeds toward product expansion — as the company hopes in the piece. Distinct from today’s Emulate X (seed talks, not a closed compliance ops raise).
My takeaway
From Mexico, the narrow read: Comp AI’s $34M Series A (Roo + Grand; ~$37.5M total) is continuous compliance ops tooling — draft policies, collect evidence, watch controls after you ship agents — with humans still approving and independent audits still required. Pen-test automation stays labeled as company. Not an AIUC certification twin. Source: TechCrunch.