From Mexico, the part of security tooling I’ve always liked least is the backlog. A scanner finds something, the alert sits there, and nobody owns the boring fix. So GitHub’s changelog entry from October 15 caught my eye: agentic autofix for code scanning alerts is now generally available.
The short version: you assign a code scanning alert to Copilot, and it tries to fix it the way a developer would. In GitHub’s words, it “explores relevant files, proposes a fix, and reruns CodeQL to confirm the fix closes the alert before opening a pull request for your review.”
The loop is the interesting part
Older one-shot fix suggestions just handed you a patch. This version runs a loop. Per GitHub, Copilot explores the relevant files, generates a proposed fix, validates it by rerunning CodeQL, iterates if needed, and then opens a draft pull request. That PR includes a summary of the fix, why it closes the alert, and the validation steps Copilot took.
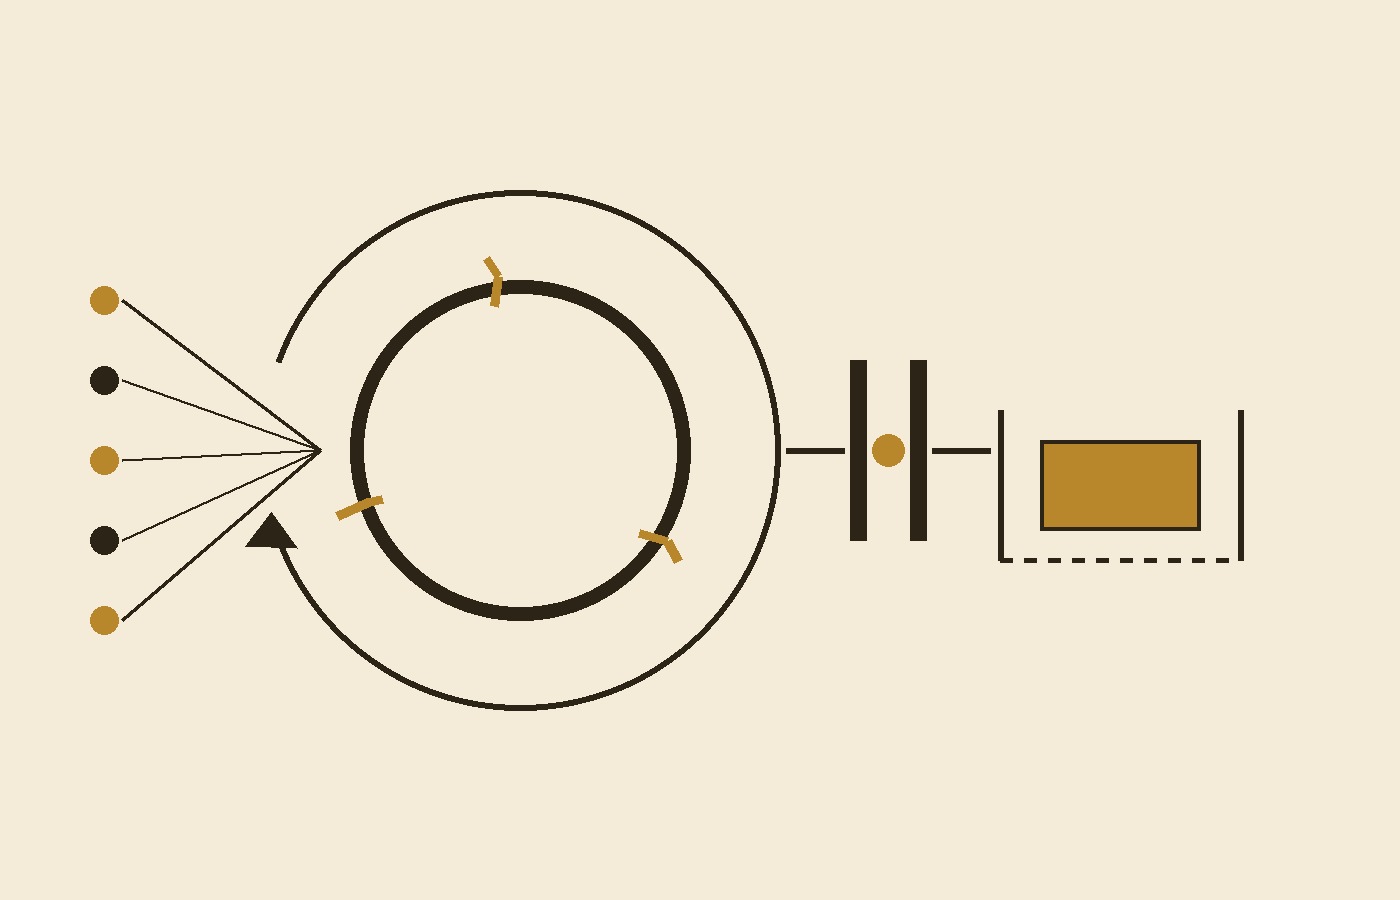
That’s the pattern I keep coming back to with coding agents: the agent should have to prove its own work against the same check that raised the problem, and a human still merges. Here the proof is the scanner itself, and the output is a draft, not a merge.
Once the PR exists, you can ask for more changes by commenting on it or through the session in the repository’s Agents tab.
How you actually use it
When it’s enabled, GitHub says the free Generate Fix option on individual alerts is replaced by an Assign to Copilot button. There are three ways in:
- From any code scanning alert on the default branch.
- From the security alert list or a security campaign, selecting up to 25 alerts for Copilot to fix together in a single pull request.
- Through the REST API, by setting the alert’s assignee to the Copilot coding agent bot.
That 25-alert batch is the bit I’d try first. Old, low-drama findings are exactly the backlog nobody wants, and one reviewable PR beats twenty-five tiny ones.
Where it stops, and what it costs
A few limits worth knowing before you get excited:
- Default branch only. Alerts found only on pull requests or other branches can’t be assigned to Copilot.
- Enterprise plumbing. It’s for GitHub Code Security and GitHub Advanced Security customers on GitHub Enterprise Cloud. An enterprise admin has to enable a new “Agentic autofix” policy, then an org or repo admin turns it on, and a Copilot billing method has to be defined.
- It isn’t free. It consumes AI Credits from your Code Security budget plus GitHub Actions minutes, and GitHub says you can set SKU-level budgets for those credits.
The same morning, GitHub also made AI Scan for pull requests generally available. It complements CodeQL by looking for vulnerabilities in PR changes for languages CodeQL doesn’t cover yet, like PHP, Shell, Terraform HCL and Dockerfiles. GitHub is clear those findings are advisory: they don’t fail the check and can’t block merges through rulesets. I like that honesty. Finding with AI and fixing with AI both end at a human decision.
My take
I don’t read this as “security is solved by agents.” GitHub doesn’t claim that either. What I read is a good design habit getting productized: give the agent a narrow job, make it re-run the exact check that failed, and make it explain itself in the PR. If you’re building your own agent workflows, steal that shape even if you never touch this feature. And keep reviewing the diff. A passing scanner tells you the alert closed, not that the change is the one you’d have made.
Featured image: “Kintsugi,” photo by Guggger, Wikimedia Commons, CC BY-SA 4.0. Cropped and resized to 1400×900 and lightly sharpened.