From Mexico — coding agents already speed up the PR. What still hurts is everything after: is this change secure, is the deploy healthy, and which of eleven merges broke checkout? On Sep 23, Cursor’s product blog and changelog ship two Teams/Enterprise bots for that last mile: Rollouts (PR → deploy → per-environment health) and Security Review (exploitable findings + proposed fix on pull requests). This is PR-and-deploy automation, not another model drop into the editor and not laptop package gating.
Rollouts — watch the change into production
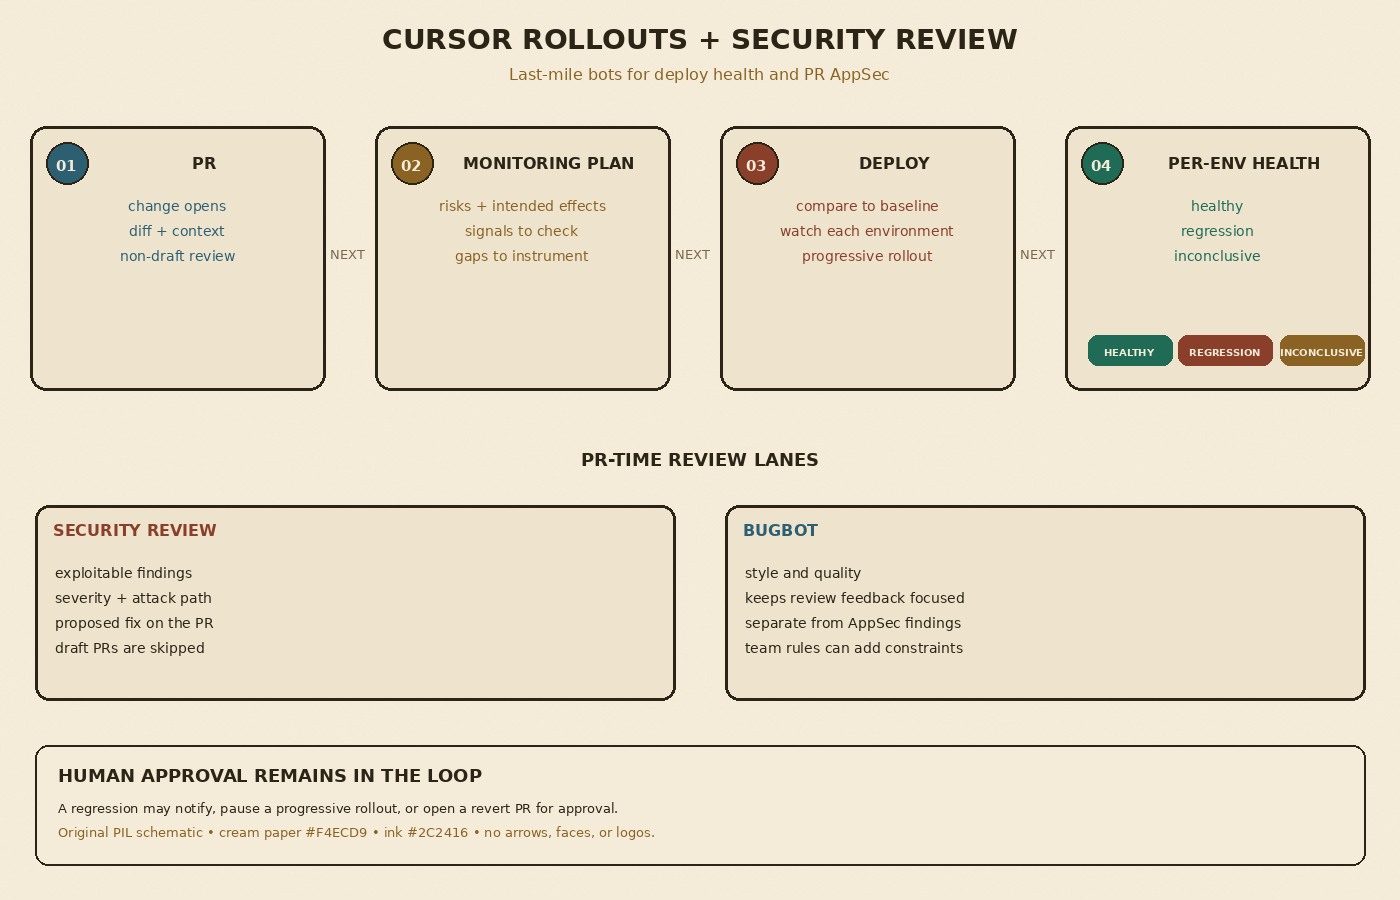
Per the changelog, Rollouts attaches a monitor to every pull request and reports change health per environment: verified healthy, regression detected, or inconclusive. You connect source control, your continuous delivery system, and telemetry (Datadog and others). When a PR opens, Rollouts reads the diff and posts a monitoring plan — risks, intended effects, signals it will check, and instrumentation gaps. Edit the plan in the PR; Rollouts uses your version.
After deploy, it compares plan signals to a pre-deploy baseline. On a regression, it can notify the author, pause a progressive rollout, or open a revert PR waiting for approval. The changelog is explicit: Rollouts does not merge or roll back on its own today. Feature-flag ramp/unramp and release-train awareness are called out as coming soon — not shipped in this release.
Security Review — AppSec on the PR; Bugbot keeps style
Security Review runs on non-draft PRs (drafts are skipped), reads the change in codebase context, and posts one review comment with exploitable bugs. Style and quality stay with Bugbot. Findings carry severity, an attack path, and a proposed fix. Out of the box it looks for injection (SQL, command, template, and related surfaces), missing or broken auth on new/changed routes — including checks that a refactor stopped running — secrets in source, SSRF and unvalidated redirects, unsafe deserialization, and dependency changes that pull known vulnerabilities. Team rules can encode repo-specific constraints.
Teams and Enterprise availability
Both bots are available on Teams and Enterprise; enable them from the automations tab. The changelog also notes a short usage-credits promo for trying Rollouts on real changes (roughly 50 changes for Teams / 500 for Enterprise for the next 10 days, per Cursor). No efficacy percentages or MTTD claims in the shipping posts — I’m sticking to what they published.
My takeaway
Agentic coding made “open the PR” cheap. The expensive part is verify and ship without guessing which change broke which region. Rollouts and Security Review are Cursor’s bet that bots should own that last mile — with humans still approving reverts and merges. If you’re already on Teams/Enterprise, the Sep 23 blog and changelog are the primary map.